
Tag
Tagged: CVE
Hosting, infrastructure, development, and SEO — written by the people doing the work.
CVE-2026-88771 and 88772: Citrix NetScaler Zero-Days Exploited for Days Before the Patch
Security
Check Point VPN and Management Server Both Hit by Pre-Auth RCE
Security
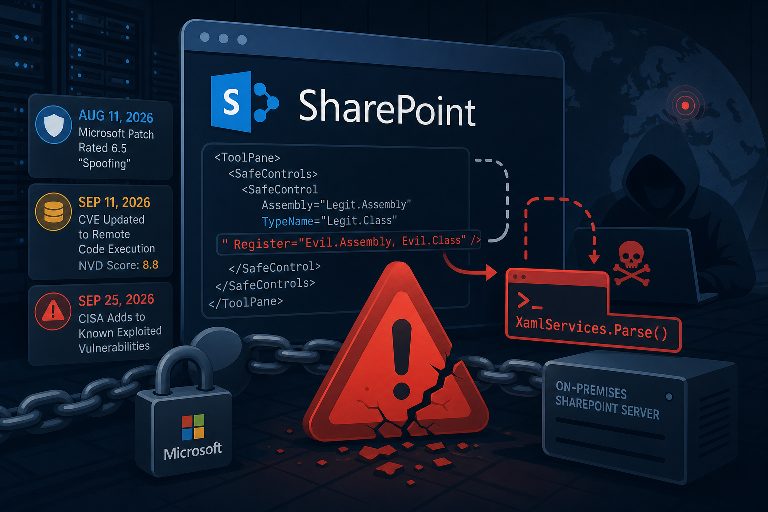
CVE-2026-65660: SharePoint's 'Spoofing' Bug Enables Code Execution
Security
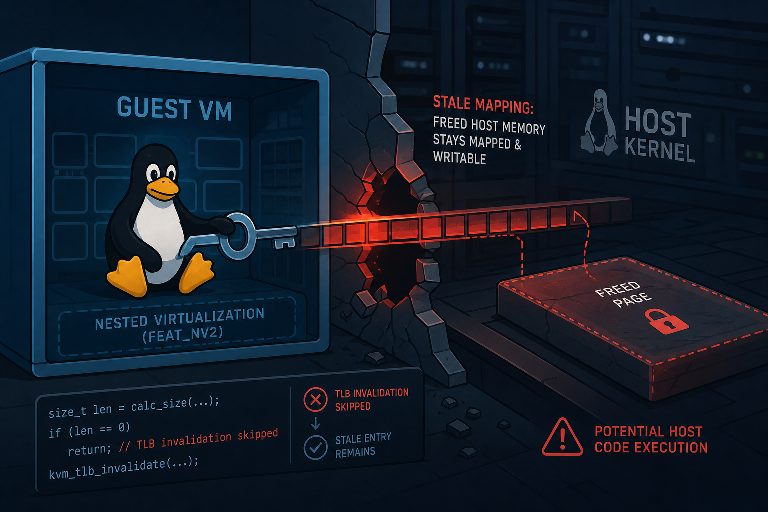
CVE-2026-89775: Linux KVM on ARM64 Lets a Guest VM Escape to the Host
Security
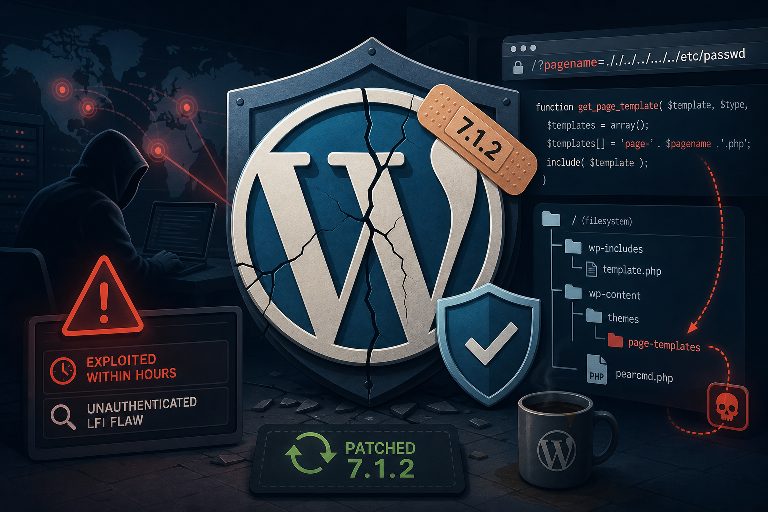
CVE-2026-87902: WordPress Core LFI Flaw Exploited Within Hours of Patch
WordPress
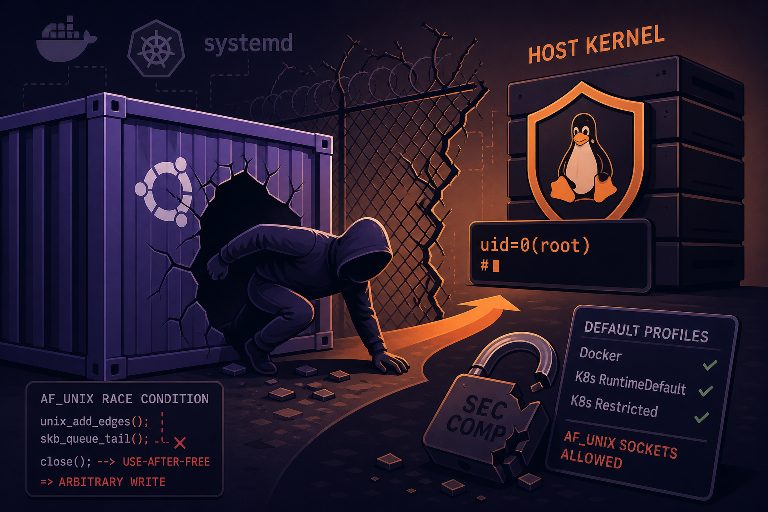
CVE-2026-80521: Ubuntu's Container Escape Has a Public Exploit and No Patch
Security
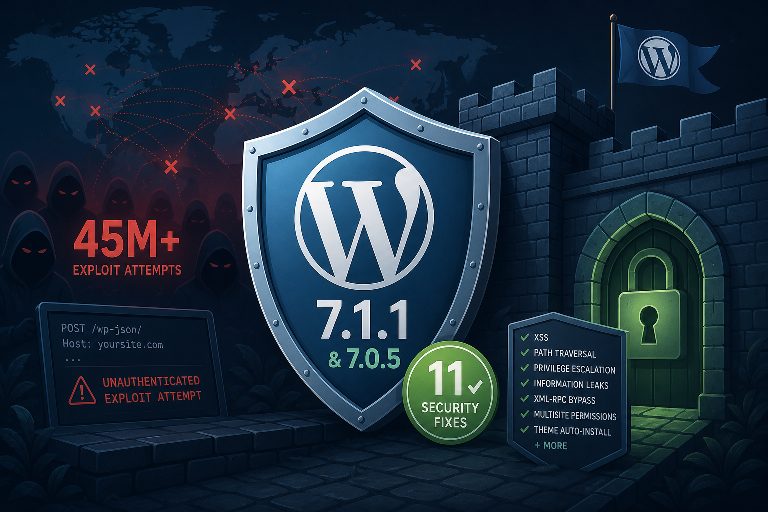
WordPress 7.1.1: 11 Security Fixes While WP2Shell Exploitation Hits 45 Million Attempts
WordPress
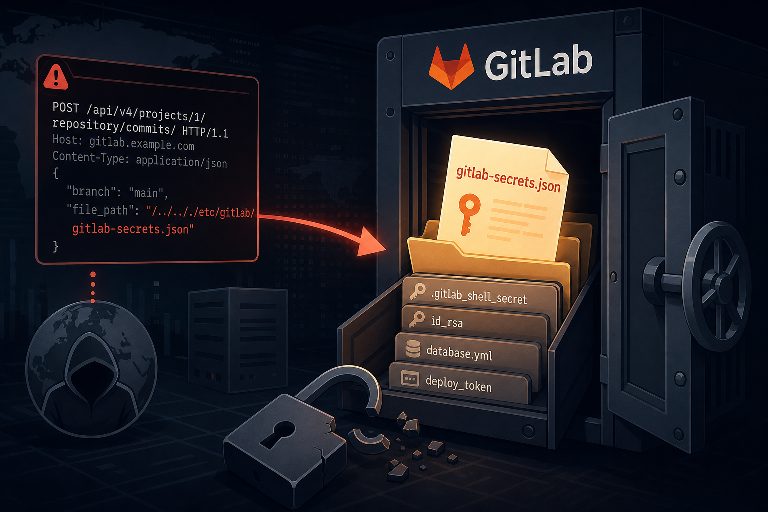
CVE-2026-85706: One HTTP Request Reads Your GitLab Secrets
Security
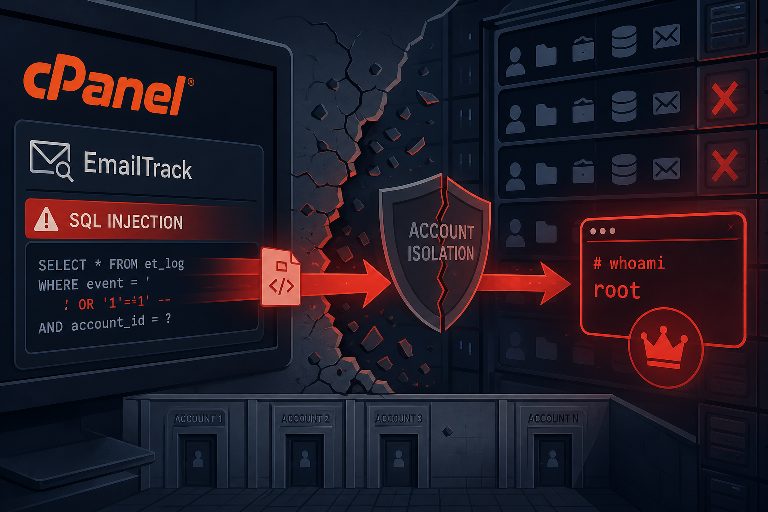
CVSS 9.9: cPanel's EmailTrack Flaw Puts Every Shared Hosting Tenant at Risk
Security
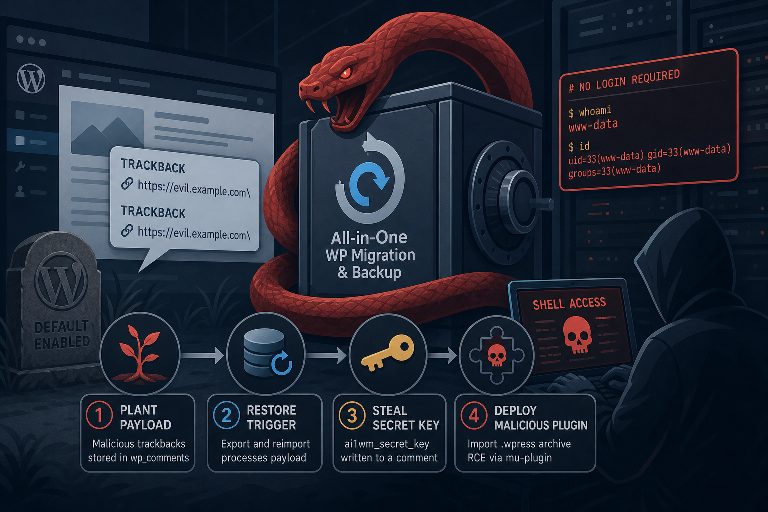
CVE-2026-19949: Your Backup Plugin Is Now an Attack Vector for 3.2 Million Sites
WordPress
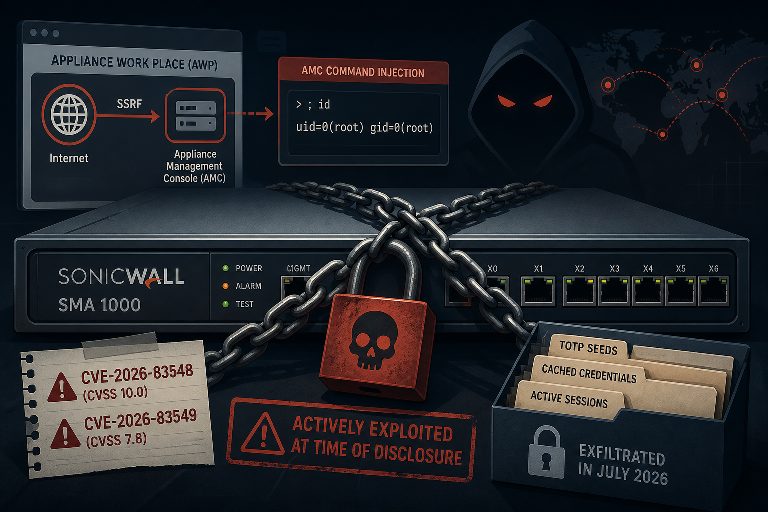
SonicWall SMA1000's Third Zero-Day Chain: Patch Now — Then Check What July Left Behind
Security
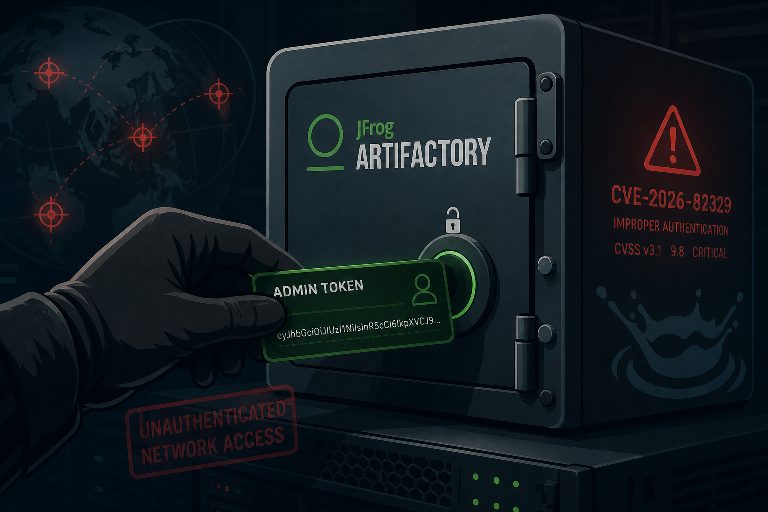
CVE-2026-82329: Attackers Are Minting JFrog Artifactory Admin Tokens Three Days After Patch
Security
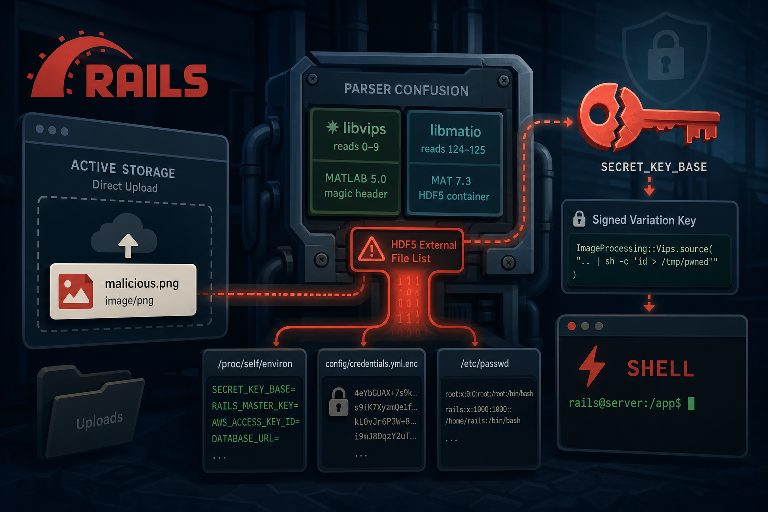
KindaRails2Shell: Active Exploitation of CVE-2026-66066 Means One Update Isn't Enough
Security
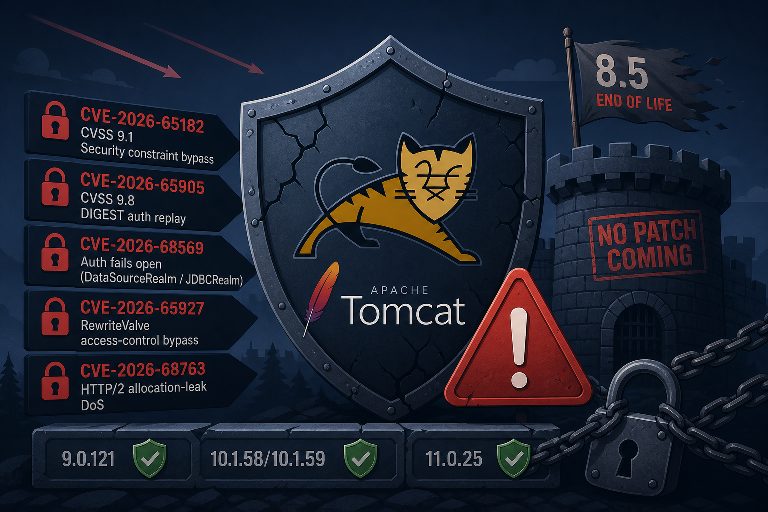
11 CVEs in One Shot: Apache Tomcat's Biggest Security Release of 2026
Security
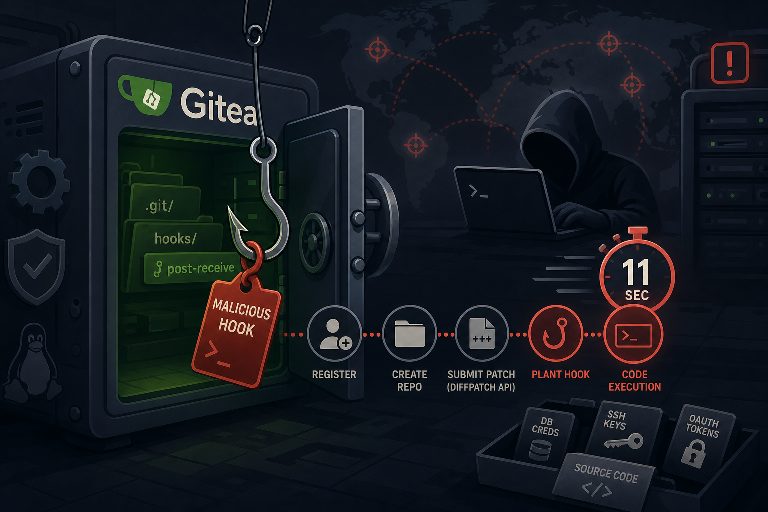
CVE-2026-60004: Gitea's Hook Injection Flaw Is Under Active Attack — Patch to 1.27.1 Now
Security